

Hi all 👋
First, I’ll be at Fintech Devcon in Denver next week. If you’ll be there and want to connect, let me know (via Twitter or fintechtldr@gmail.com)!
Second, @regulatorynerd and I had a blast recording a new Fintech Layer Cake episode with Jareau Wadé, Chief Growth Officer at Finix. He has some incredible insights from his payments pioneer experience. Give a listen!

Substack says your email will clip this edition; click here to read in browser!
Tornado Cash & “Privacy” 🌪️

OFAC sanctioned Tornado Cash (Tornado) and 40+ Ethereum and USDC wallets associated with it. Tornado is a crypto mixer, a service that helps users hide the source of funds by intermingling streams of crypto. And it’s a decentralized protocol. Think: open-sourced code run by many, not a single business entity.
The sanction was based on Tornado materially assisting cyber activity that threatens the US, including a North Korean state-sponsored hacking group. Practically, it means Tornado and the relevant wallet addresses were added to the Specially Designated Nationals (SDN) list. And it’s generally illegal for Americans to transact with anyone on the SDN list.

This is the first time OFAC has sanctioned a protocol (i.e., smart contract), and has led crypto companies like Circle to blacklist Tornado wallets for their users. And Netherland officials have also arrested at least one Tornado developer for his involvement with the protocol.
Some thoughts. 🍿
First, it’s worth mentioning mixers can be used for legitimate purposes; it’s not all North Korean hackers hiding ill-gotten gains. One example: an employee who gets paid in BTC might not want their employer to view all of their transactions; a mixer lets the employee retain their privacy. Your employer doesn’t see what you spend your USD salary on; why should it be different from crypto?
This is the crux of policy making: balancing the good and the bad. DDT was a great insecticide, but we banned it because the bad outweighed the benefits. Similarly, having some bad aspects doesn’t mean a technology or tool should necessarily be banned.
Second, some have pointed out that, yes, centralized actors can help cut off access to Tornado, but that’s not enough to shut the decentralized protocol down. It’s a key feature (or bug, depending on your view) of decentralized autonomous orgs: if they’re truly decentralized, it’s very, very hard to stop them.
But that’s not compelling; it’s impossible to completely shut off criminals’ access in the traditional finance world, too, especially when research suggests current AML laws don’t catch over 99% of criminal proceeds. Adding a terrorist to the SDN list isn’t foolproof. But it does add friction. That’s the point. In the real world, almost nothing works perfectly. Making it harder for folks to use Tornado at all achieves OFAC’s goal, even if imperfect. It’s not different from traditional finance.
Third, lots of folks are up in arms about the sanctions, saying OFAC has gone too far. They argue OFAC is targeting neutral tools, not the bad actors the SDN list is meant for. Others argue it might not even be constitutional; the 9th Circuit has ruled code is constitutionally protected speech and the Supreme Court has said spending money can be, too. So the sanctions impinge upon fundamental rights, they argue.
But, of course, Americans don’t have an absolute right to free speech; the government can limit it in circumstances, especially where it encourages imminent illegal acts. And you can also argue that Tornado isn’t a “neutral tool,” but instead an entity – a DAO – that can be put on the SDN list.1
Fourth, anti-sanction sentiment argues the OFAC move violates privacy rights. Yes, Americans (allegedly) have a right to privacy when you read between the lines of the US Constitution (fun fact: privacy rights aren’t explicitly in the US Constitution, but they’re the first thing in California’s).
However.
Privacy is not the same as anonymity, especially in financial services.2 Privacy is “the government can’t see my bank transactions (without a warrant).” Anonymity is “no one, including the government, knows this bank account is mine; it wouldn’t even matter if the government had a warrant.”3
And in traditional financial services, you have privacy rights, not anonymity rights. Otherwise, KYC wouldn’t be a thing.
Related thought: in a sense, you can say blockchains like bitcoin’s exchanged privacy for anonymity. Transactions aren’t private, but users can be anonymous.4 Contrast that with your bank account where transactions aren’t publicly viewable, but have to give your identity to the bank.
None of this is meant to make judgment calls about whether this OFAC move is right or wrong. I just want to call out the nuance that’s been omitted from the Tornado policy dialogues.
Oh also, one fun quirk: it’s illegal to deal with anyone blocked on the SDN list. But Tornado is a protocol. So you can send crypto into it and specify the wallet funds end up in. So someone sent crypto through Tornado to Coinbase’s CEO, Jimmy Fallon, Logan Paul and others, effectively exposing them to sanctions risk.
Hello Digit, Goodbye “Never”
Another piece of fintech news making waves: the CFPB issued a consent order against Hello Digit (Digit). The company offers an app that algorithmically helps you budget, save, and invest. The order is premised on Digit misrepresenting claims related to overdrafts, and says Digit:
Misrepresented its saving algorithm by claiming it would never transfer more than a user could afford,
Claimed to offer reimbursement for overdrafts but didn’t deliver, and
Told users it wouldn’t keep any interest earned on consumer funds after moving to a subscription model, but retained some interest in practice.

Two thoughts.
First, notice the problem with the above screenshot? You can’t say “we never do X, period” and in literally the next sentence say “if X happens, we’ll reimburse you.” Those two things aren’t consistent.5
Making sure your site and marketing materials aren’t misleading or making overly bold claims is one thing a good fintech lawyer will protect you against. Here’s a free pro-tip (not legal advice, not your lawyer!): don’t use words like “never,” “always,” and “guarantee.”

Second, Oportun (who acquired Digit) issued a statement about the news, saying overdraft fees only affected 0.008% of members. Some fintech folks have said the order seemed overly harsh. But, again, if you say something never happens and it does…then you’re factually incorrect, even if they’re isolated incidents.
It’s also worth keeping in mind that a single overdraft fee might mean someone doesn’t have enough for rent or food for their kids that evening.
Third, this tweet (and thread) from Alex Johnson got me thinking:
Alex is right: anyone who’s read anything the Bureau has put out under Director Rohit Chopra, you will probably tell you the tone is usually, uhh, not Midwest-nice (can you tell I’m from WI?). I’ve heard others describe the Bureau’s tone as aggressive and hostile. And one key theme of the CFPB under Chopra is using blogs and press releases as a bully pulpit.
Problem: If you’re harsh about everything, are you harsh about anything?
Your ire loses signal and weight if it’s applied to everything. Alex’s tweet got me wondering: does the CFPB have a “boy who cried wolf” problem now? When a new CFPB release comes out now, I’m increasingly hearing and seeing lawyers and fintech operators respond with “oh, it’s just the CFPB release with a harsh tone, who knows what it actually means.”
Maybe it’s scaring financial services into better compliance on average. But there’s a point where folks throw up their arms and shrug because they’re unsustainably over-complying out of fear. Maybe the Bureau is watering down its bully pulpit powers.

Elsewhere (non-crypto)...
I’m going to try out a new style for the “Elsewhere” sections: more narrative than bullet list. If you like or dislike it, let me know!
The CFPB issued an interpretive rule saying, in effect, tech firms and digital marketing providers are subject to CFPB jurisdiction if they do more than just offer the “time and place” for running ads. This could mean, for example, if a company like Facebook lets advertisers pick the location, gender, etc. of targets, the CFPB can go after them for UDAAP violations (like, say, ads that have discriminatory impact by only advertising to Facebook groups primarily composed of white users). It gives the CFPB another hook to go after big tech, among others.
In “let’s protect data better” news, the CFPB confirmed that inadequate safeguarding of consumer data may count as an unfair act or practice. Additionally, banking trade groups asked the CFPB to supervise data aggregators (think: Plaid), per Bloomberg.
In BNPL news, CA’s financial regulator settled with BNPL provider Four over providing BNPL services without a license (CA requires BNPL providers to get a license if there are >4 installments, finance charges, and other features). Elsewhere, Rohit Chopra said the CFPB will scrutinize Apple’s expansion into BNPL, including whether the move is anti-competitive, per the FT.
Senators Durbin and Marshall introduced a bill that would generally prohibit credit card issuers from restricting the number of card networks transactions can be processed on.
Ford applied for an ILC charter, per AmBanker. It’s not the first time, and could be a bellwether for other non-financial companies to do the same. I wouldn’t hold your breath for an approval.
For the payments nerds 🤓, the Fed finalized guidance for deciding who can access Fed master accounts. Master accounts are required for sending funds over Fed rails (i.e., Fedwire, FedACH, and FedNow). The short version: institutions subject to less regulatory oversight will be more thoroughly vetted by the Fed. Don’t get too hyped up for fintech, though; you still need to be a bank to be eligible.
Goldman Sachs is being investigated by the CFPB over its credit card billing, payments, advertising, and reporting practices, per its 10Q. Goldman currently only manages a GM co-branded card and the Apple Card.
In oopsies news 🤦: For ~3 weeks this year, Equifax sent incorrect credit scores to lenders, affecting millions, per WSJ. Also 🤦: The CFPB issued a consent order, including a $37.5M penalty, against US Bank after employees opened lines of credit and deposit accounts for consumers without their knowledge, among other issues, due in part to a sales rewards system that incentivized opening such accounts. Gotta wonder how long this kind of account opening will remain de rigueur among big banks. 🤔

Last oopsie: NY’s financial regulator fined Robinhood $30M for violating AML and cybersecurity regulations, thanks in part to the company experiencing high growth without adding sufficiently mature compliance guardrails, per CoinDesk. Maybe they should have listened to the Fintech Layer Cake episode on building a compliance function?

Elsewhere (in crypto)...
The FDIC isn’t happy about crypto. 😡 First, they sent a cease and desist to Voyager, demanding the company stop claiming they themselves were insured (vs. their partner bank), all funds at Voyager were insured, and that the FDIC would insure against Voyager’s failure itself.
Second, the FDIC also released a fact sheet and advisory covering crypto companies’ claims of FDIC insurance. Spoiler: crypto isn’t FDIC-insured, and companies shouldn’t mislead users about it. Third, the FDIC is apparently pressuring banks not to service crypto companies, and Sen. Toomey wants them to back off, per AmBanker.
Speaking of Voyager: a bankruptcy court rules that customer USD deposits at its partner bank weren’t part of Voyager’s assets for bankruptcy purposes, reinforcing the importance of using FBO accounts, per WSJ.
In “maybe regulators will regulate crypto via regulation instead of enforcement” news, Fed. Governor Bowman said the Fed is working on guidance for bank’s interested in crypto activities like custody services, purchases/sales, collateralized loans, and stablecoin issuance. And the Fed released guidance saying banks that want to engage in crypto activities need to determine if the activities are legal and notify the Fed beforehand. This mirrors similar guidance from the OCC.
Lots of Coinbase news. The DOJ brought an insider trading case against a former Coinbase manager who allegedly gave tips on which assets the platform would list in the future. The key news from that case: DOJ claims at least 9 of 25 crypto assets involved were securities. Also, Coinbase itself is being probed by the SEC over whether it listed seven tokens that should have been registered as securities, per Bloomberg. Lastly, a proposed class action against Coinbase alleged they had insufficient cybersecurity practices that let accounts be drained by hackers and scams, per Bloomberg.
In other “crypto exchanges in hot water” news, Kraken is under investigation for allegedly violating sanctions by letting users in Iran and other prohibited countries use the exchange, per the New York Times.
Sui Generis (Fun Finds)


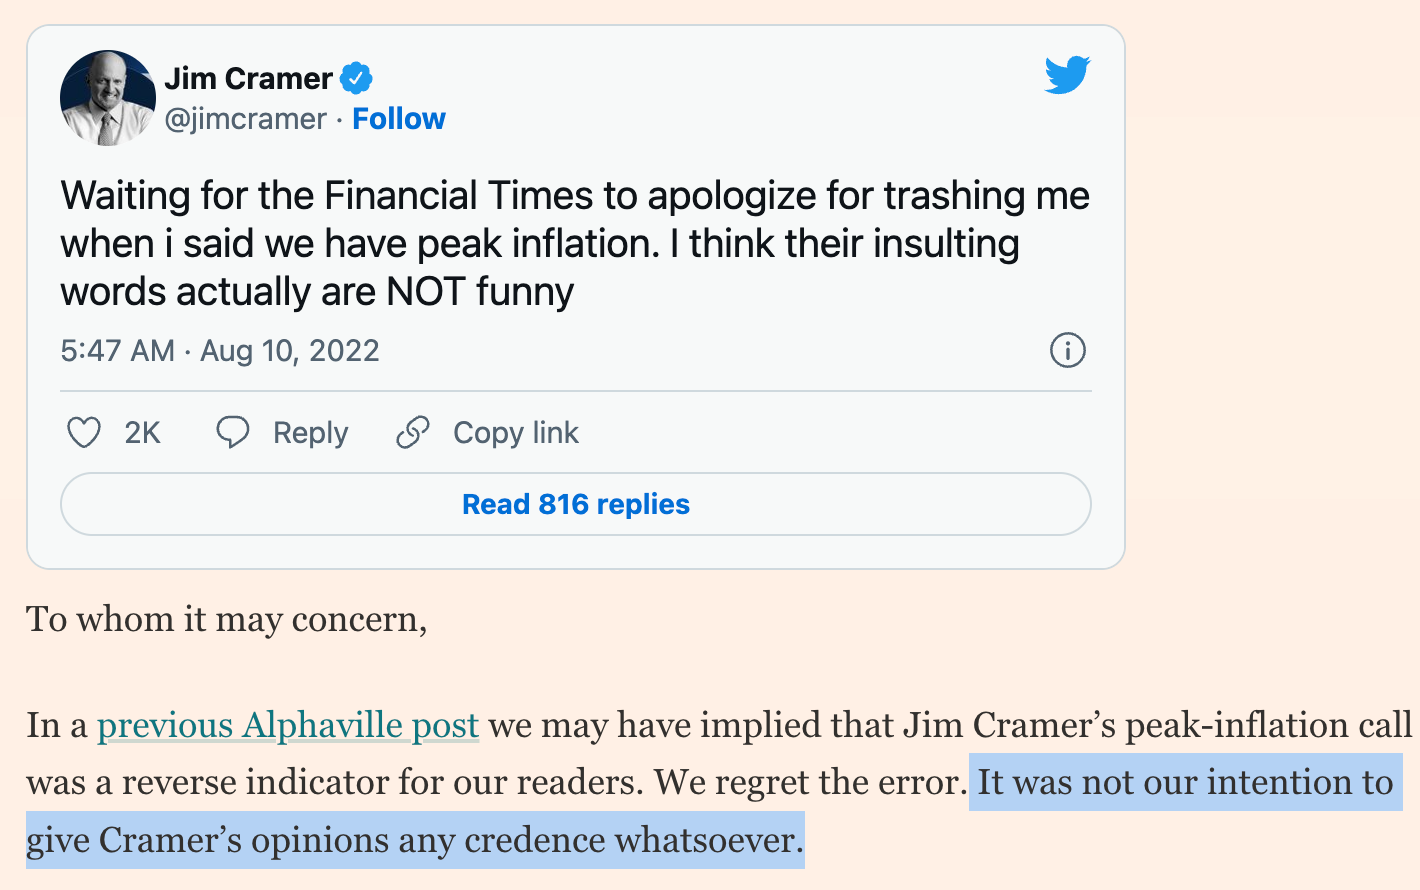
The Financial Times issued an amazing apology:

Hi. I’m Reggie. I’m a fintech product lawyer at Lithic.
Reach out (email or Twitter) if you’re interested in any of the following:
Sponsoring the newsletter
Early stage fintech looking to raise
Collaborating
Just want to say hey!
Any views expressed are my own (well, sort of? I mean, they’re based on laws and regulations, so they’re not really “mine”?). Nothing here is legal or financial advice. Don’t get your legal advice from Substack, duh.
See, for example, how Consensys defines a DAO as a “community-led entity.” Though you can argue it’s not an entity and take ethereum.org’s framing that it’s a “community.” But then we’re going down a semantic rabbit-hole arguing over whether a community counts as an entity, etc.
Credit where credit is due: this phrasing came from whip-smart colleagues of mine at Privacy.com (though not in the crypto context). I can’t claim credit for it, but I do love it.
I recognize crypto advocates argue that this is the point, anonymity protects you against illegitimate government actions masquerading as legitimate. I’m not making judgment calls here, just calling out the under-discussed difference between privacy and anonymity rights.
Though, of course, a user’s identity can be inferred from their transaction history, and all you need is one tie to a user to identify them.
You can get into semantics about what “afford” means in their claims, but it seems reasonable to say triggering overdraft means a user couldn’t afford a transaction.